ADCS ESC17: Find Server Templates That Accept Any Name
ADCS ESC17 is a certificate template for TLS servers that lets the requester choose the name, needs no approval and lets broad groups enroll. Every domain machine trusts your enterprise CA. So anyone who can enroll may potentially get a trusted certificate for a server they don't run. This post shows you how to find these templates, narrow who can use them and decide where names should come from.
| Priority | High, because anyone who can enroll may potentially get a trusted TLS certificate for a server they don't run |
|---|---|
| What decides it | A template with a server authentication purpose, a name supplied in the request, no approval and a broad group that can enroll |
| Who's affected | Forests with web server templates opened to Domain Users or Domain Computers so anyone could request TLS certificates |
| Fix | Narrow who can enroll. Then build names from AD or require approval. Revoke certificates issued for names the requester doesn't run |
Check it now: which templates issue server certificates for any name?
# Runs as any domain user. Lists templates where the requester supplies the subject,
# the certificate works for server authentication and no approval or signature is required.
Import-Module ActiveDirectory -ErrorAction Stop
$pks = "CN=Public Key Services,CN=Services,$((Get-ADRootDSE).configurationNamingContext)"
# Everyone, NETWORK, INTERACTIVE, Anonymous, Authenticated Users, This Organization, Users
$low = 'S-1-1-0', 'S-1-5-2', 'S-1-5-4', 'S-1-5-7', 'S-1-5-11', 'S-1-5-15', 'S-1-5-32-545'
# Domain Users, Domain Guests and Domain Computers of any domain
$lowRid = '^S-1-5-21-\d+-\d+-\d+-51[345]$'
$enroll = [guid]'0e10c968-78fb-11d2-90d4-00c04f79dc55', [guid]::Empty
$full = [System.DirectoryServices.ActiveDirectoryRights]::GenericAll
# Server Authentication, Any Purpose
$server = '1.3.6.1.5.5.7.3.1', '2.5.29.37.0'
$cas = Get-ADObject -SearchBase "CN=Enrollment Services,$pks" -LDAPFilter '(objectClass=pKIEnrollmentService)' -Properties certificateTemplates
# 0x1 means the requester supplies the subject
Get-ADObject -SearchBase "CN=Certificate Templates,$pks" -LDAPFilter '(msPKI-Certificate-Name-Flag:1.2.840.113556.1.4.803:=1)' -Properties pKIExtendedKeyUsage, msPKI-Enrollment-Flag, msPKI-RA-Signature, nTSecurityDescriptor |
    ForEach-Object {
        $t = $_
        $ekus = @($t.pKIExtendedKeyUsage | Where-Object { $_ })
        if ($ekus.Count -gt 0 -and @($ekus | Where-Object { $_ -in $server }).Count -eq 0) { return }
        # 0x2 in msPKI-Enrollment-Flag means a certificate manager approves each request
        if (($t.'msPKI-Enrollment-Flag' -band 2) -or $t.'msPKI-RA-Signature') { return }
        $enrollers = $t.nTSecurityDescriptor.GetAccessRules($true, $true, [System.Security.Principal.SecurityIdentifier]) |
            Where-Object {
                $_.AccessControlType -eq 'Allow' -and (
                    (($_.ActiveDirectoryRights -band $full) -eq $full) -or
                    (($_.ActiveDirectoryRights -band 'ExtendedRight') -and $_.ObjectType -in $enroll))
            } |
            ForEach-Object {
                $sid = $_.IdentityReference
                try { $name = $sid.Translate([System.Security.Principal.NTAccount]).Value } catch { $name = $sid.Value }
                if ($sid.Value -in $low -or $sid.Value -match $lowRid) { "$name (low privilege)" } else { $name }
            }
        [pscustomobject]@{
            Template    = $t.Name
            PublishedOn = ($cas | Where-Object { $_.certificateTemplates -contains $t.Name }).Name -join ', '
            EKUs        = if ($ekus.Count) { $ekus -join ', ' } else { '(none: any purpose)' }
            Enrollers   = ($enrollers | Sort-Object -Unique) -join '; '
        }
    }
Runs as any domain user with the ActiveDirectory module. It lists templates where the requester supplies the subject and the certificate works for server authentication, with nothing requiring approval. A row with a CA in PublishedOn and a (low privilege) enroller is the ESC17 pattern.
You checked one setting. The free scan checks the rest of your on-prem AD in a few minutes.
Nothing gets installed on your domain controllers. Only HTTPS leaves your network.
What ADCS ESC17 is
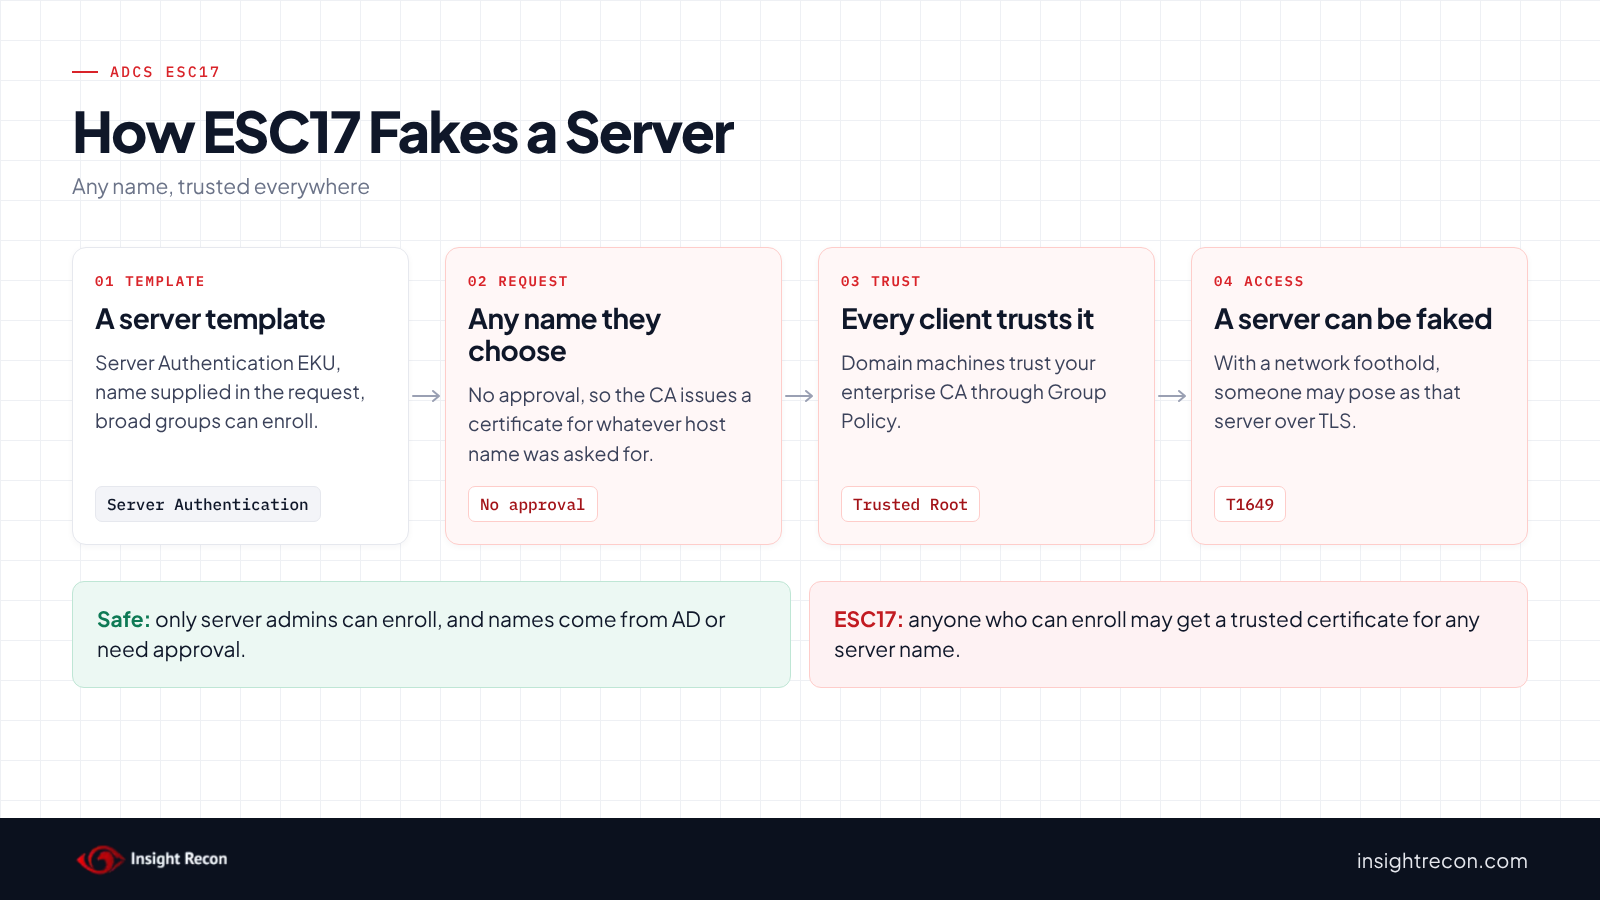
ESC17 is the server-side cousin of ESC1. Alexander Neff and Phil Knüfer of DigiTrace introduced it at TROOPERS26. A template becomes ESC17 when four things line up:
- The requester supplies the subject. Microsoft's msPKI-Certificate-Name-Flag reference describes the flag that tells the client to "supply subject information" in the request. With it, the CA also takes the SAN from the request, where TLS clients look for the server name.
- The certificate works for TLS servers. Its purposes include Server Authentication (
1.3.6.1.5.5.7.3.1, defined in RFC 5280), Any Purpose or no purpose at all. - Nothing checks the request. No certificate manager approval and no authorized signature is required.
- A broad group can enroll. For example, Domain Users, Domain Computers or Authenticated Users.
In other words, ESC1 is the same pattern on templates built for sign-in, covered in our ADCS ESC1 post. A template that allows both purposes is both.
Why ADCS ESC17 is dangerous
Your CA is trusted everywhere
Microsoft's page on enterprise certification authorities says an enterprise CA "uses Group Policy to propagate its certificate to the Trusted Root Certification Authorities certificate store for all users and computers in the domain." As a result, a certificate from an ESC17 template looks fully legitimate to every domain machine.
Any server name is on the table
Because the requester picks the name, they may potentially get a certificate for an intranet site, an update server or a domain controller's LDAPS name. With a foothold on the network path, someone could then pose as that server over TLS. DigiTrace's talk did this with a WSUS server's name to attack clients that get updates over HTTPS. Our WSUS security post covers that path. MITRE ATT&CK tracks the certificate side as T1649, Steal or Forge Authentication Certificates. It tracks the interception as T1557, Adversary-in-the-Middle.
It looks like normal TLS
Clients see a valid chain to your own root. Therefore, no browser warning appears. Instead, only the CA's issuance records show that the requester never ran that server.
Find ESC17 in your forest
Read the quick check results
The quick check above returns one row per matching template. In most forests, only a few templates show up.
What to look for: any row with a CA in PublishedOn and a (low privilege) group in Enrollers. Also look at custom groups with many members. An unpublished template can't be used today. Still, anyone who can change a CA's templates could publish it. For version 1 templates such as Web Server, also read our ADCS ESC15 post.
Check what the template already issued
Run this on the CA. It lists every certificate the template issued, with who asked for it and the name in it.
# Run on the CA as a CA administrator or certificate manager, with the AD module installed.
# Replace WebServerCustom with the template name from the quick check.
Import-Module ActiveDirectory -ErrorAction Stop
$pks = "CN=Public Key Services,CN=Services,$((Get-ADRootDSE).configurationNamingContext)"
$t = Get-ADObject -SearchBase "CN=Certificate Templates,$pks" -LDAPFilter '(cn=WebServerCustom)' -Properties msPKI-Cert-Template-OID, msPKI-Template-Schema-Version
if (-not $t) { throw 'Template not found.' }
# The CA database records version 1 templates by name and later versions by OID
$id = if ([int]$t.'msPKI-Template-Schema-Version' -le 1) { $t.Name } else { $t.'msPKI-Cert-Template-OID' }
certutil -view -restrict "CertificateTemplate=$id,Disposition=20" -out 'RequestID,RequesterName,CommonName,NotBefore,SerialNumber' csv | ConvertFrom-Csv
What to look for: a CommonName for a server the requester doesn't manage. For example, a user account requesting the name of a domain controller or an update server. In that case, open those certificates in the CA console and check the SAN on the Details tab too.
Check ADCS ESC17 with Insight Recon
The free scan includes Server Authentication Template with Enrollee-Supplied Subject in ADCS (ESC17), a High check. It lists every published template where the enrollee supplies the subject and the certificate allows server authentication (Server Authentication, Any Purpose or no EKU), with no approval or authorized signature required. A template that only sets the SAN flag passes, since the CA ignores that flag. A broad group also has to hold Enroll, all extended rights or full control. Broad groups here are Everyone, Anonymous, Authenticated Users, NETWORK, INTERACTIVE, This Organization and Users. Domain Users, Domain Guests and Domain Computers from any domain count too. A deny entry only cancels a right when it comes earlier on the template and names that same group, Everyone, Authenticated Users or NETWORK. Owners and accounts that can only edit the template show up under ESC4 instead. For each template, the finding shows the groups and the rights they hold. It also comes with the Hacker Insight, remediation steps and compliance mappings.
Know what the ADCS ESC17 check doesn't decide
Some things are still yours to check. The check skips templates no CA publishes. If it can't read a CA's template list, it treats every template as published, so it may list one nobody can request right now. When unpublished templates would match, a note on the result says how many. They show up in the script above with an empty PublishedOn. It also doesn't count custom groups with many members, so check those yourself. It reads templates only, so run the issued script above to see what the CA already handed out.
Related checks beyond ESC17
- User-controlled certificate template subject in ADCS (ESC1), the same pattern on sign-in templates. Our ADCS ESC1 post covers it.
- Schema V1 Certificate Template Allows Arbitrary Application Policy in ADCS (ESC15), old version 1 server templates such as Web Server. Our ADCS ESC15 post covers it.
- Unrestricted certificate template modification rights in ADCS (ESC4), who can turn a safe template into this one. Our ADCS ESC4 post covers it.
You can see what the findings look like in our sample report. The full list is in our check library.
Find every template that hands out server certificates for any name, plus the other ADCS attack paths.
It runs from any Windows machine that can reach your DCs, with a standard domain account. Every core AD check is free for one domain.
Before you change the template
Find out who requests certificates from it. Then pick where names should come from for each kind of requester.
Find out who uses it
The issued script shows who requested certificates and for which names. For example, you may see server admins requesting TLS certificates by hand, plus appliances or load balancers that enroll on a schedule. Then ask each owner which names they need.
Pick where names come from
- Domain-joined Windows servers: build the name from AD. The certificate then carries the computer's own DNS name. That way, it can't name anything else.
- Appliances and non-domain systems: keep the supplied name. However, grant Enroll to a small server admin group and require certificate manager approval.
- Nobody: stop issuing the template.
Save the current state
The Enroll script saves the template's permissions to an SDDL file. Similarly, the approval script prints the current flag value. Keep both until you're sure nothing broke.
Fix ADCS ESC17 safely
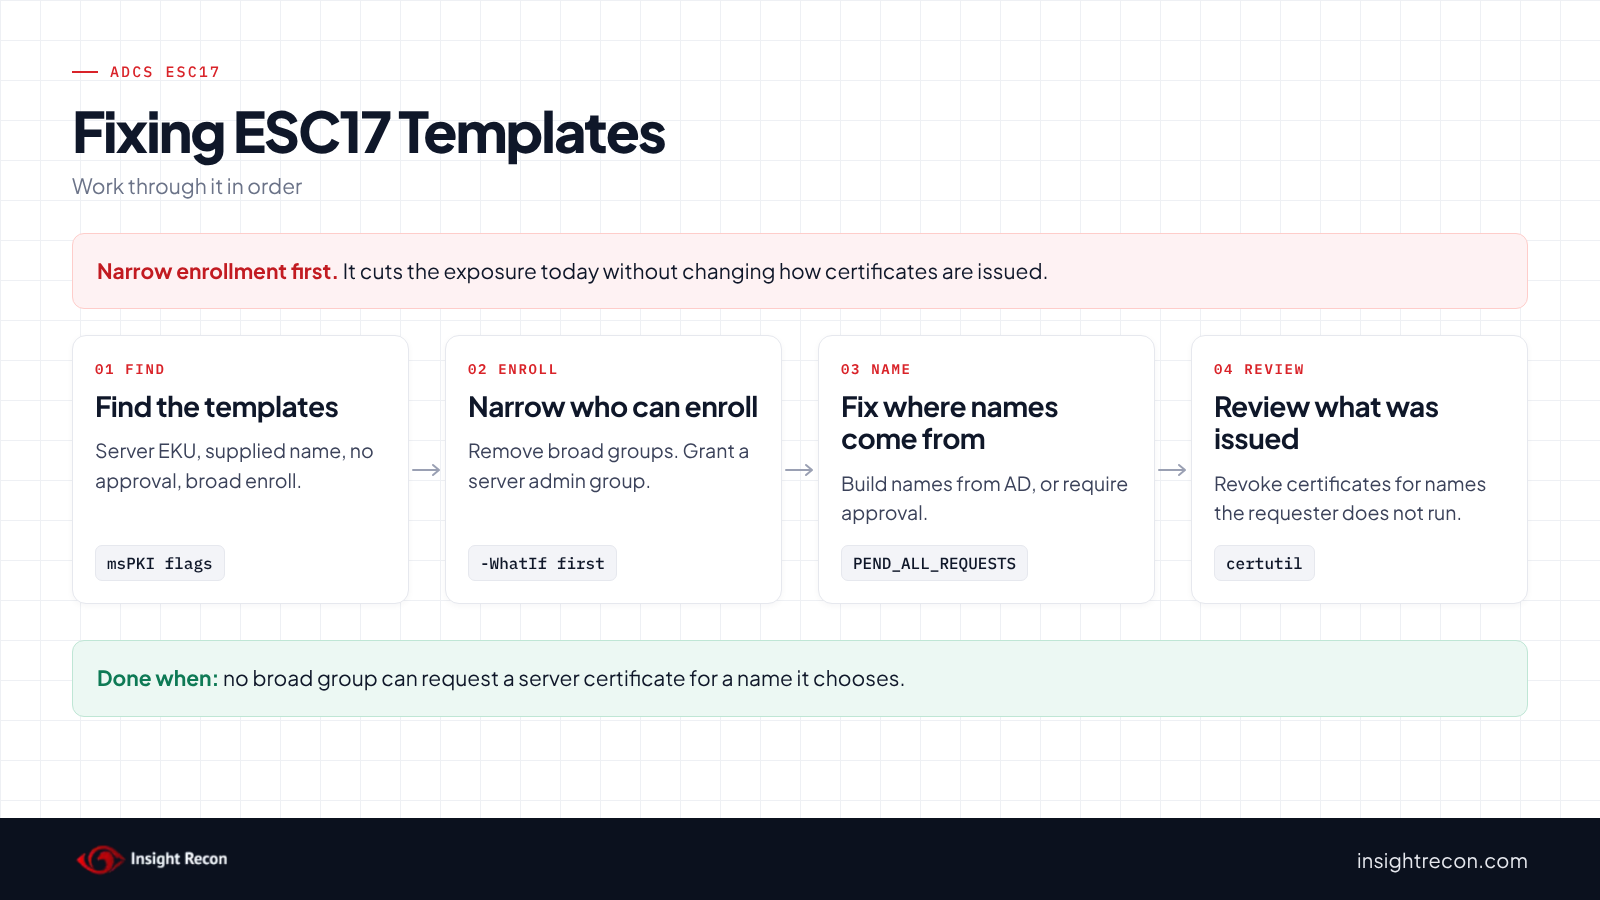
Each change script below is a dry run with -WhatIf. Drop that to apply. They need Enterprise Admins. Change WebServerCustom to your template's name.
1. Remove broad Enroll grants
This removes Enroll from Everyone, Authenticated Users, Domain Users, Domain Computers and the other broad groups on one template. It saves the current permissions first and warns about grants it can't safely split.
# Dry run. Drop -WhatIf to apply.
# Needs Enterprise Admins, or permission to change the template's security.
Import-Module ActiveDirectory -ErrorAction Stop
$pks = "CN=Public Key Services,CN=Services,$((Get-ADRootDSE).configurationNamingContext)"
$t = Get-ADObject -SearchBase "CN=Certificate Templates,$pks" -LDAPFilter '(cn=WebServerCustom)'
if (-not $t) { throw 'Template not found.' }
$low = 'S-1-1-0', 'S-1-5-2', 'S-1-5-4', 'S-1-5-7', 'S-1-5-11', 'S-1-5-15', 'S-1-5-32-545'
$lowRid = '^S-1-5-21-\d+-\d+-\d+-51[345]$'
$enrollRights = [guid]'0e10c968-78fb-11d2-90d4-00c04f79dc55', [guid]'a05b8cc2-17bc-4802-a710-e7c15ab866a2', [guid]::Empty
$path = "AD:$($t.DistinguishedName)"
$acl = Get-Acl -Path $path -ErrorAction Stop
# Saves the current permissions so you can put them back
$acl.Sddl | Set-Content -Path ".\$($t.Name)-acl.sddl"
foreach ($ace in $acl.GetAccessRules($true, $false, [System.Security.Principal.SecurityIdentifier])) {
    if ($ace.AccessControlType -ne 'Allow' -or ($ace.IdentityReference.Value -notin $low -and $ace.IdentityReference.Value -notmatch $lowRid)) { continue }
    if ($ace.ActiveDirectoryRights -eq 'ExtendedRight' -and $ace.ObjectType -in $enrollRights) {
        [void]$acl.RemoveAccessRuleSpecific($ace)
    } elseif ($ace.ActiveDirectoryRights -band [System.DirectoryServices.ActiveDirectoryRights]::ExtendedRight) {
        Write-Warning "$($ace.IdentityReference) holds Enroll combined with other rights. Fix it on the template's Security tab."
    }
}
Set-Acl -Path $path -AclObject $acl -ErrorAction Stop -WhatIf
What to look for: the dry run should show only the broad groups' Enroll entries being removed. Afterward, add Enroll for the small group that really requests these certificates.
2. Require approval where names stay supplied
This turns on certificate manager approval for one version 2 or later template. As a result, every request waits in the CA's Pending Requests until someone checks the name.
# Dry run. Drop -WhatIf to apply.
# Needs Enterprise Admins, or write rights on the template object. Version 1 templates can't be changed this way.
Import-Module ActiveDirectory -ErrorAction Stop
$pks = "CN=Public Key Services,CN=Services,$((Get-ADRootDSE).configurationNamingContext)"
$t = Get-ADObject -SearchBase "CN=Certificate Templates,$pks" -LDAPFilter '(cn=WebServerCustom)' -Properties msPKI-Enrollment-Flag, msPKI-Template-Schema-Version
if (-not $t) { throw 'Template not found.' }
if ([int]$t.'msPKI-Template-Schema-Version' -le 1) { throw 'Version 1 template. Duplicate it to a version 2 copy first.' }
# Note the current value so you can put it back
$t.'msPKI-Enrollment-Flag'
# 0x2 is CT_FLAG_PEND_ALL_REQUESTS: every request waits for a certificate manager
Set-ADObject -Identity $t -Replace @{ 'msPKI-Enrollment-Flag' = ($t.'msPKI-Enrollment-Flag' -bor 2) } -ErrorAction Stop -WhatIf
What to look for: the printed value is the current flag. The dry run shows the new value with 0x2 added. Version 1 templates can't be changed, so duplicate those first.
3. Build names from AD for domain servers
In the Certificate Templates console, duplicate the template for domain-joined servers. On the Subject Name tab, choose Build from this Active Directory information with the DNS name. Then publish the copy and move those servers to it.
4. Revoke certificates for names the requester doesn't run
For each certificate the issued script turned up, revoke it on the CA with certutil -revoke and its serial number. Then review recent connections to the server it named.
Keep ADCS ESC17 closed
Microsoft's list of PKI events to monitor covers issuance and template changes. These events need CA auditing turned on.
- Watch issuance. Event 4887 fires for each issued certificate and includes the subject. Alert when a server template issues a name on your list of sensitive hosts.
- Watch template loads. Event 4898 fires when a CA loads a template. Alert when a template you retired comes back.
- Re-run the scan. It flags any server template that broad groups can enroll in again.
ADCS ESC17 checklist
- Can a broad group enroll in any server template that takes the name from the request?
- Do domain-joined servers get names built from AD?
- Do templates that still take supplied names require approval?
- Did you review what each template already issued?
- Did you revoke certificates for names the requester doesn't run?
- Is CA auditing on, with alerts for events 4887 and 4898?
A "yes" on the first question means anyone in that group may potentially get a trusted certificate for any server in your forest.
Compliance mapping
| Framework | Reference | Why it applies |
|---|---|---|
| MITRE ATT&CK | T1649, T1557 | Steal or Forge Authentication Certificates and Adversary-in-the-Middle. A requester gets a trusted certificate for a server they don't run, which lets them pose as it from the network path. |
| CIS Controls v8 | Control 4, Control 6 | Secure configuration of enterprise assets and access control management. Templates and enrollment rights are both in scope. |
| NIST CSF 2.0 | PR.AA-01, PR.AA-05 | Identities and credentials are managed and access follows least privilege. A server's identity should come from its owner. |
ADCS ESC17 FAQ
What is ADCS ESC17?
A server certificate template that lets broad groups request a certificate for any name, with no approval.
How is ESC17 different from ESC1?
ESC1 gives a certificate that signs in as another user. ESC17 gives a certificate that poses as another server.
Does strong certificate mapping stop ESC17?
No. Strong mapping protects sign-in to AD. ESC17 certificates pose as servers. TLS clients check the name and that the chain leads to a trusted root.
Can I keep supplied names for appliances?
Yes, with a small enroll group and certificate manager approval. That way someone checks each name before the CA issues it.
Does Insight Recon check for ADCS ESC17?
Yes. The free scan includes Server Authentication Template with Enrollee-Supplied Subject in ADCS (ESC17), along with the other ADCS checks.
See which templates hand out server certificates for any name.
It runs from any Windows machine that can reach your DCs, with a standard domain account. Every core AD check is free for one domain.
Not ready to scan?
AD Signal is our monthly look at what's changing in AD security and how real domains score. Read the latest report.
References
- [MS-CRTD]: msPKI-Certificate-Name-Flag Attribute
- Enterprise Certification Authorities (Microsoft Learn)
- RFC 5280, section 4.2.1.12: Extended Key Usage
- TROOPERS26: ESC17, Using ADCS to Attack HTTPS-Enabled WSUS Clients
- Securing PKI, Appendix A: Events to Monitor
- MITRE ATT&CK: T1649 Steal or Forge Authentication Certificates
- MITRE ATT&CK: T1557 Adversary-in-the-Middle