Find the holes attackers use to take over Active Directory
Insight Recon runs 155+ read-only checks against your domain. Every finding explains how an attacker would use it and how to fix it, PowerShell included.
- Free for one domain with every on-prem finding. No Domain Admin needed.
- Only AD metadata leaves your network. See what's sent and what isn't
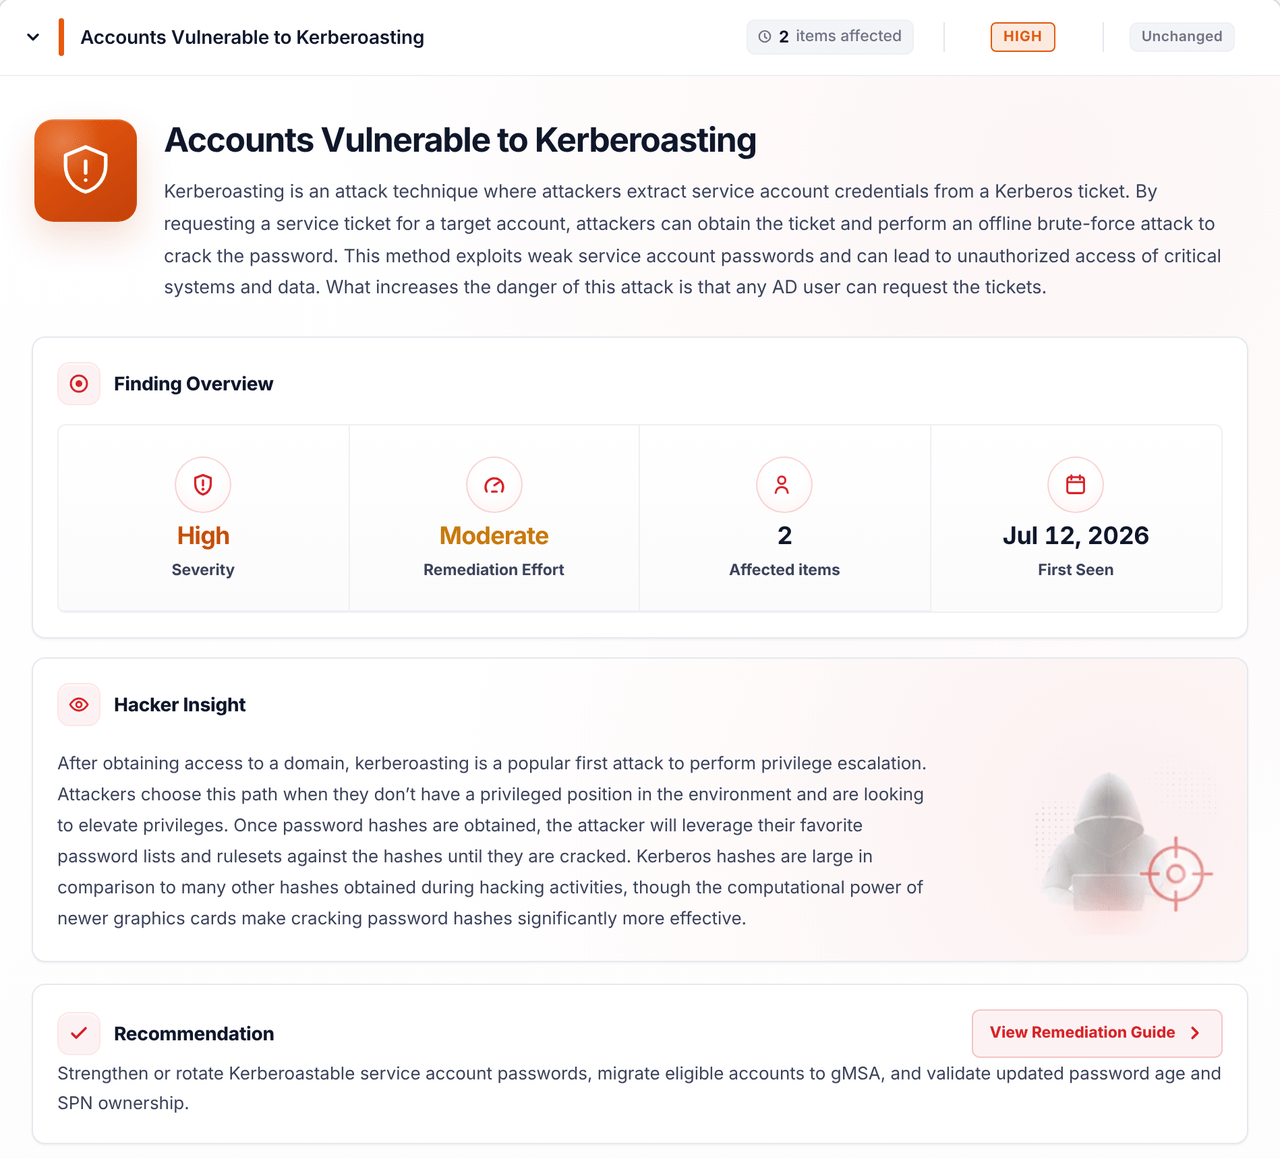
After obtaining access to a domain, kerberoasting is a popular first attack to perform privilege escalation. Attackers choose this path when they don't have a privileged position in the environment and are looking to elevate privileges.
Strengthen or rotate Kerberoastable service account passwords, migrate eligible accounts to gMSA, and validate updated password age and SPN ownership.
Used by teams at


What a scan can uncover
-
CriticalCertificate services
User-controlled certificate template subject (ESC1)
A regular user can request a certificate that lets them log in as a Domain Admin.
-
HighAccounts
Accounts vulnerable to Kerberoasting
Any domain user can request a ticket for these accounts and crack the password offline if it's weak.
-
HighDelegation
Unconstrained delegation
An attacker who takes over one of these servers gets a reusable login ticket (TGT) for anyone who's connected to it, admins included.
-
HighDomain controllers
LDAP signing not enforced on domain controllers
An attacker can relay a captured login to a domain controller and make changes as that user.
-
HighKerberos
Stale krbtgt account password
If this password has ever been stolen, tickets forged with it still work.
-
HighDomain settings
Non-admin users can add computer accounts
Any user can add computers to the domain, which several escalation paths rely on.
The average first scan turns up about 40 findings, including many of the above. See more in the sample report →
Every finding comes with the fix
- The attacker's side
How it gets abused so you know why it's worth fixing.
- What to line up first
Who owns each account and what depends on it so the fix doesn't take anything down.
- The fix
PowerShell for one account or a reviewed list, plus click-by-click steps in ADUC. Bulk scripts run with
-WhatIfuntil you take it off. - Proof it worked
Checks to run after the change and the evidence an auditor will want.
- Where it maps
MITRE ATT&CK, NIST, CIS, STIG and ANSSI, plus a CSV of the affected objects.
The rest of that Kerberoasting finding from up top, cut down to fit
- Service owner identification and sign-off for each affected account.
- Inventory of services and applications dependent on each account's credentials.
- Locate the affected service account in Active Directory Users and Computers.
- Reset the password. Enter a strong, complex password of at least 25 characters.
- Update the dependent service with the new password in Services.msc or the application's configuration.
- Restart the service and confirm it starts successfully.
Get-ADUser -Identity <account> -Properties PasswordLastSet- Verify the dependent service is running and authenticating successfully.
- Run Insight Recon AD against the same scope to confirm the finding is resolved.
155+ checks from people who've spent years breaking into AD
Accounts and passwords
Kerberoasting, AS-REP roasting, stale passwords and accounts that don't need one.
Privileged access
Who can take over your admin accounts and who can pull every password hash with DCSync.
Certificate services and PKI
Every AD CS escalation from ESC1 through ESC16, plus your trusted roots and weak certificate crypto.
Kerberos and delegation
Delegation of every kind, plus how old your krbtgt password is.
Group Policy
Who can edit your GPOs and what the settings hand an attacker.
Domains and trusts
Trust settings and SID filtering, including trusts nobody uses anymore.
Configuration and hygiene
SMBv1, Print Spooler on DCs, LAPS coverage and legacy protocols.
Hybrid identity Standard
24 checks on what Entra Connect leaves in AD, like the sync account and AZUREADSSOACC$.
Written by the offensive security team at Breach Point. Browse every check →
Run your first scan in a few minutes
- Create a free account
It takes about a minute.
- Download the scanner
It's a portable Windows scanner. Nothing gets installed on your domain controllers or endpoints.
- Run it as a standard user
Use any domain-joined Windows machine and a standard domain account. It needs LDAP or LDAPS to a domain controller.
- Read your report
Most scans finish in a few minutes. Big domains can take about half an hour. Grab a coffee.
AD metadata: the objects and settings the checks look at.
Password hashes and Kerberos tickets never leave your network. Neither does your NTDS.dit file.
It's stored in Microsoft Azure, encrypted in transit and at rest. You can export or delete it any time. Close your account and it's gone within 30 days.
We've completed our SOC 2 Type 1 audit. Type 2 is next, with the same auditor.
Want it on a schedule? Standard adds a Windows agent that runs scans for you. Can't send anything out of your network at all? Ask us about an air-gapped setup.
Free gets you every on-prem finding
Find what's wrong in one domain and fix it.
- Every on-prem finding, in full, with no cap
- Hacker insight and remediation steps on each one
- Risk posture score and quick wins
- Executive summary export and the HTML report
- One domain, with your latest scan kept
For teams keeping one domain clean over time.
- Everything in Free
- Scan history with trends and a diff between scans
- 24 hybrid identity checks
- Account risk scores
- Scheduled scans with the Windows agent
- Your logo on the report
For consultants and MSSPs, or your own team with more than one domain.
- Up to 50 client domains per term
- Rights to use it on client work
- White-label reports
- A Linux scanner alongside the Windows one
- Unlimited users
Need SSO or more than 50 domains? That's Enterprise.
Before you ask
Do I need Domain Admin to run it?
No. A standard domain user on a domain-joined Windows machine is all it needs.
Will the scan change anything or set off alerts?
It won't change anything. The scan is read-only.
It can set off alerts, though. It reads a lot of AD over LDAP in a short time, which some security tools flag as reconnaissance. Give whoever watches your alerts a heads-up first.
How is it different from PingCastle or Purple Knight?
Both are solid tools. Ours is built around the fix: PowerShell for one object or a reviewed list, plus the checks and evidence that prove it's done. Our comparisons go through the details.
Can I run it on a client's domain?
Not on Free or Standard. Client work needs the Auditor plan (up to 50 domains per term) and written authorization from each client. See the plans.
Got another question? Email our team.
Go see what's hiding in your domain
Free for one domain. No sales call needed, but we're happy to talk.